Fractional CISO · FinTech & Payments
Fractional CISO leadership for growing FinTech and payments companies.
When bank partners, enterprise customers, or your board expect more from security, you need experienced leadership that takes ownership.
NTD Consulting helps establish security priorities, lead improvements, and develop credible evidence to address bank, customer, audit, and board requirements.
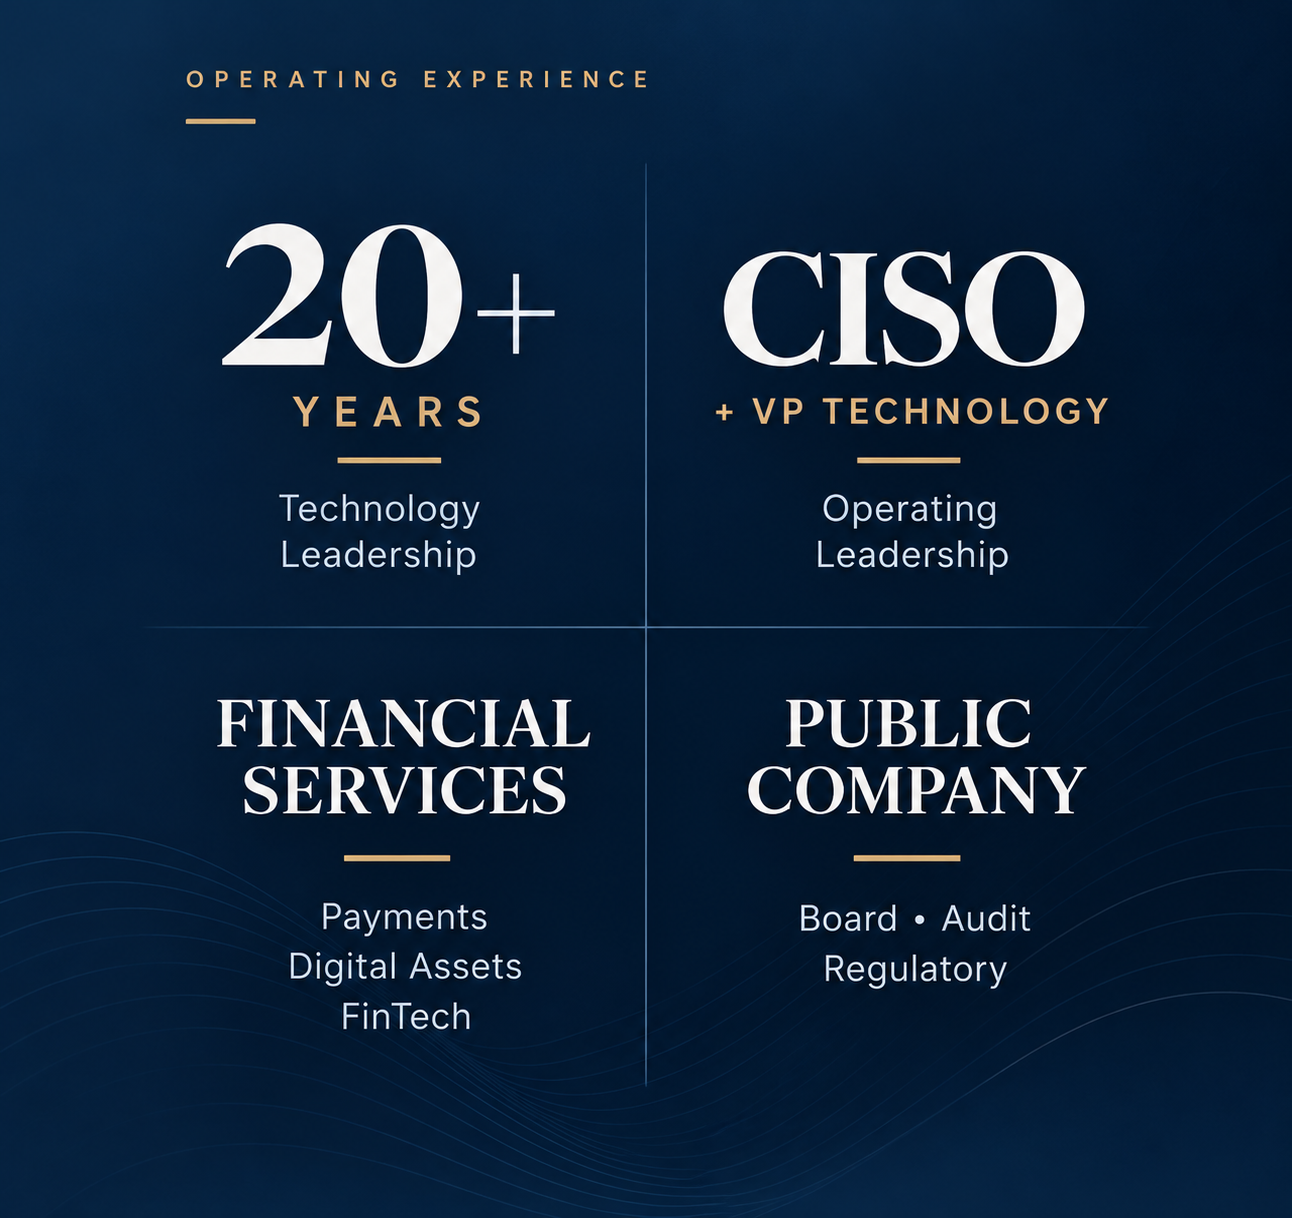
Our approach draws on experience leading technology and cybersecurity inside regulated financial-services businesses.
A conversation about your business and security priorities, with a clear next step if there is a fit.
When to bring in NTD
Security requirements are growing. Ownership needs to grow with them.
Bank or customer diligence is approaching
You need credible answers, supporting evidence, and a plan for addressing gaps.
The CTO no longer has enough time to own security
Important decisions and improvements need an accountable leader.
An audit is exposing gaps
Policies, controls, evidence, and remediation need coordinated ownership.
The board needs a clear picture of risk
Leadership wants to understand what matters, what is improving, and which decisions need attention.
Engagements
Two ways to work with NTD
A defined requirement
Security Readiness Sprint
Focused leadership for bank diligence, a customer security review, audit preparation, or a board assessment.
- Clarify the requirement and review available evidence
- Identify material gaps and prioritize action
- Coordinate agreed improvements with your team
- Deliver a readiness summary and remaining-risk assessment
Fixed scope and fee. Timing, deliverables, and client responsibilities are agreed before work begins.
Discuss a readiness sprint →Sustained ownership
Ongoing Fractional CISO Leadership
A designated security leader working alongside your executives and technical teams.
- Lead the agreed security roadmap and investment priorities
- Coordinate improvements with internal teams and specialists
- Support risk decisions and stakeholder requirements
- Establish regular executive and board reporting
Monthly retainer. Responsibilities, capacity, escalation arrangements, and client resources are defined together.
Discuss ongoing leadership →How NTD works
A clear path from security concerns to accountable action.
01
Understand
Establish business priorities, immediate requirements, critical services, and current security ownership.
Output: Current-state assessment.
02
Prioritize
Identify the risks, evidence gaps, and decisions that deserve attention first.
Output: Risk register and 90-day roadmap.
03
Execute
Lead agreed improvements with your teams and service providers, with clear owners and deadlines.
Output: Tracked actions and supporting evidence.
04
Report
Give leadership a clear view of progress, remaining risks, and decisions requiring attention.
Output: Executive dashboard and decision log.
The first 30 days establish the starting point
For an ongoing engagement, the initial priorities are understanding the program, agreeing the top risks, and establishing the roadmap and reporting cadence. Early implementation depends on scope, access, and available resources.
Experience behind the practice
Security leadership grounded in operating experience.
Prior leadership experience
Public-company FinTech
Experience leading technology and cybersecurity at a Nasdaq-listed crypto FinTech, including security policies, audit coordination, and executive reporting.
Consulting engagement
SOC 2 preparation
Consulting work for a network services provider: preparation of SOC 2 evidence, policies, and business continuity and disaster recovery documentation.
Cybersecurity Dashboard
A clear view of security risk, progress, and the decisions leadership needs to make.
- Risk exposure and trends
- Security improvement progress
- Control maturity across key domains
- Budget status and investment priorities
- Decisions requiring board attention
Illustrative dashboard with sample data. Client reporting is tailored to each organization’s priorities and agreed measures.

Specialist oversight
Focused expertise for digital assets and AI.
Digital-asset security
Security leadership for businesses handling digital assets, with attention to custody arrangements, transaction authorization, privileged access, provider dependencies, and incident readiness.
Depending on scope: transaction and trust-boundary mapping, authorization review, and an executive incident tabletop.
Explore digital-asset advisory →
AI governance
Practical oversight of AI use across employees, products, and vendors: where AI is used, what data it touches, who owns the risk, and which safeguards are appropriate.
Depending on scope: an AI inventory, risk classification, approval workflow, and vendor evidence review.
Explore AI governance →
Either specialty can support an ongoing fractional CISO engagement or a separately scoped advisory project.
Research informing our work
Exploring better visibility into emerging risk.
Mirino Labs researches and develops security technology for AI visibility, cloud identities, and emerging enterprise risk. Relevant research can inform NTD's advisory work. Any use of development-stage tools is separately discussed and scoped with the client.
Fit
Where we fit
- FinTech, payments, and digital-asset companies under regulatory pressure
- Companies preparing for SOC 2, PCI DSS, or sponsor-bank diligence
- Teams that have outgrown ad-hoc security but are not ready for a full-time CISO
- Boards and investors who want security reported in business terms
Not the right fit
- Companies looking for a penetration test or a one-off audit
- Teams that want a policy binder to file and never open again
- Organizations seeking a compliance stamp without fixing the underlying program
Start with your immediate priority
What does your security program need to address next?
Tell us about the requirement, deadline, or leadership gap creating pressure. We will discuss your current security ownership and whether a focused readiness sprint or ongoing fractional CISO engagement fits.
A conversation about your business and security priorities, with a clear next step if there is a fit.